The WireLens root certificate
Why WireLens needs a trusted certificate to read inside HTTPS, and how to install, trust, export and remove it.
To show you what is inside HTTPS, WireLens presents its own certificate for each host it decrypts. Those certificates are signed by a root certificate that WireLens creates on your device the first time you use it, and your device accepts them only once you trust that root.
| Field | Value |
|---|---|
| Common name | WireLens CA, then the date it was created and the device in brackets: WireLens CA (12 Oct 2026, iPhone). A Mac uses its own name, an Android phone its model: WireLens CA (12 Oct 2026, Pixel 9) |
| Organization | Routecore LLC |
| Organizational unit | WireLens |
A certificate created by an older version keeps the name it was made with: WireLens Root CA, sometimes followed by a date and a device name.
The private key is generated on your device and stays there. Every Mac, iPhone and Android phone has its own, which is why trusting it on one device does nothing for another. Only your user account can read the key file. It is left out of iPhone and Android backups: a phone restored from a backup creates a new certificate.
The iPhone profile carries the same name as the certificate, so after you regenerate it, VPN & Device Management shows which profile is the current one. Delete the older one.
On the Mac#
The Setup Assistant's Certificate step trusts it the first time you open WireLens: click Install… and confirm with Touch ID or your password. That trusts it for your user account, which is what Safari, Chrome, Edge, Arc and most Mac apps check.
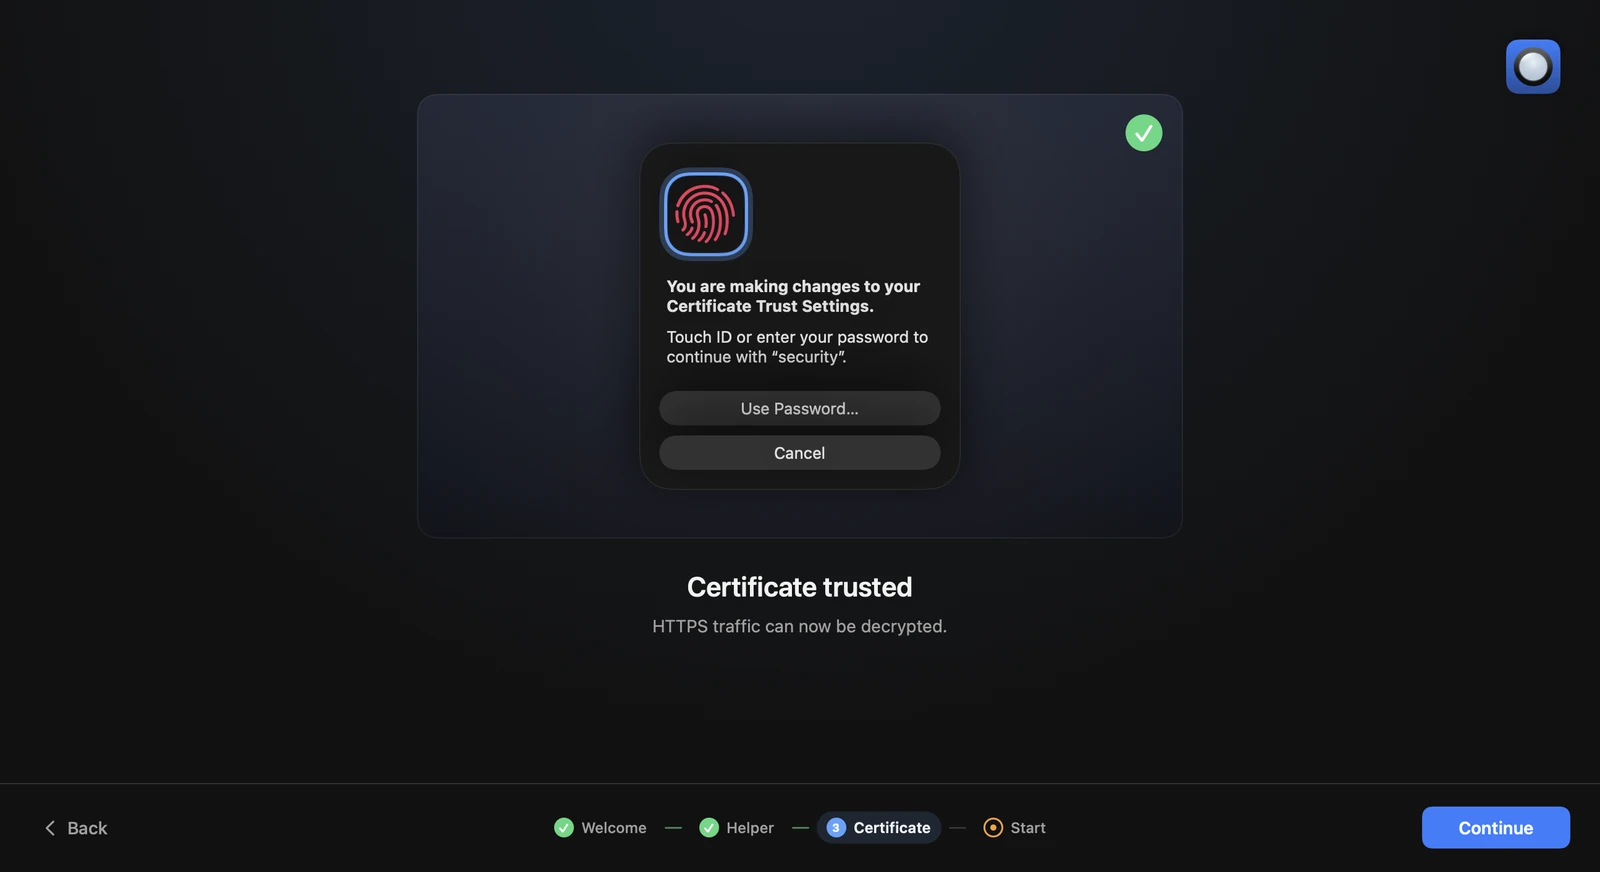
Other ways to do the same:
- Settings ▸ Certificate shows whether the certificate is missing, installed but not trusted, or trusted. Under Install, Trust for this user only ▸ Install… opens the same pictured steps, and Trust for all users ▸ Install… covers every account and system services with an administrator password. Certificate ▸ Install for All Users… in the menu bar does the same.
- By hand: export the certificate, open it in Keychain Access, expand Trust and set When using this certificate to Always Trust.
Browsers and runtimes that keep their own list#
Safari, Chrome, Edge, Arc and most Mac apps use the macOS keychain and need nothing more. The rest have to be told:
| Client | How it trusts the WireLens certificate |
|---|---|
| Firefox | Certificate ▸ Install into Firefox |
| Node.js | NODE_EXTRA_CA_CERTS pointing at the certificate |
| Python | REQUESTS_CA_BUNDLE or SSL_CERT_FILE |
| Ruby, Rust | SSL_CERT_FILE |
| Java and the JVM | A truststore made with keytool |
| Go | The macOS keychain. SSL_CERT_FILE is ignored on macOS. |
| curl | --cacert or CURL_CA_BUNDLE |
| iOS Simulator | Tools ▸ iOS Simulators installs it into each one |
Client setup has each of these ready to paste, and Tools ▸ Client Setup fills in the exact paths on your Mac.
On iPhone and iPad#
WireLens's setup guide walks through this with a picture of every screen. Set up WireLens on iPhone and iPad has the same steps with real screenshots.
- In WireLens, open the setup guide and tap Download Profile. iOS asks whether to allow a configuration profile. Tap Allow, then Close.
- Open Settings, tap Profile Downloaded near the top, then Install, and confirm with your passcode and Install twice more.
- Go to Settings ▸ General ▸ About ▸ Certificate Trust Settings and switch on the entry that starts with WireLens CA. Tap Continue.
- Go back to WireLens. It notices and restarts capture, and decryption begins.
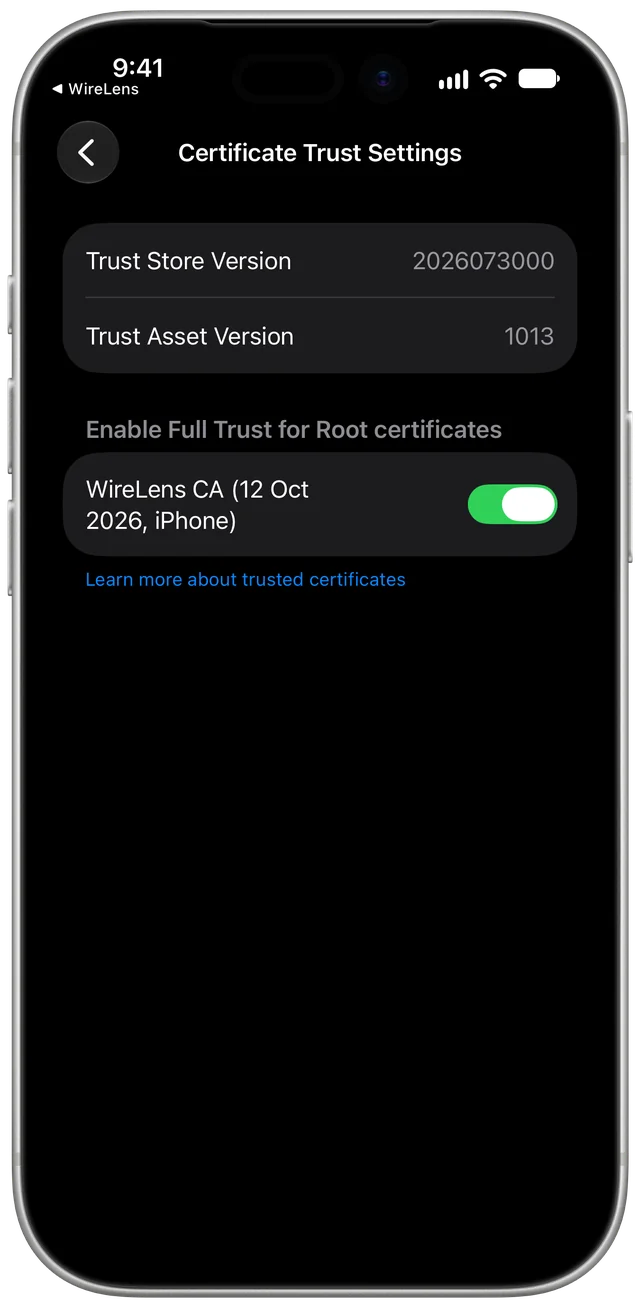
Step 3 is the one people miss. iOS installs the profile without trusting it for HTTPS until you turn on full trust.
The profile can be downloaded with or without capture running. While capture runs you can also open http://wire.lens/ in Safari to reach the install page. Other browsers show a note asking you to open it in Safari, because only Safari hands the profile to Settings.
An iPhone that uses your Mac as its proxy#
That setup needs the Mac's certificate, not the phone's. See Capture other devices.
On Android#
- Open Settings ▸ Setup Guide in WireLens and tap Save to Downloads. The file is
WireLens-CA.crt. - Tap Open Security Settings, or in Android Settings go to Security & privacy ▸ More security & privacy ▸ Encryption & credentials ▸ Install a certificate ▸ CA certificate. Searching Settings for "CA certificate" also finds it. Android needs a screen lock for this.
- Tap Install anyway and pick the file.
- Go back to WireLens. The Setup Guide shows the certificate as installed.
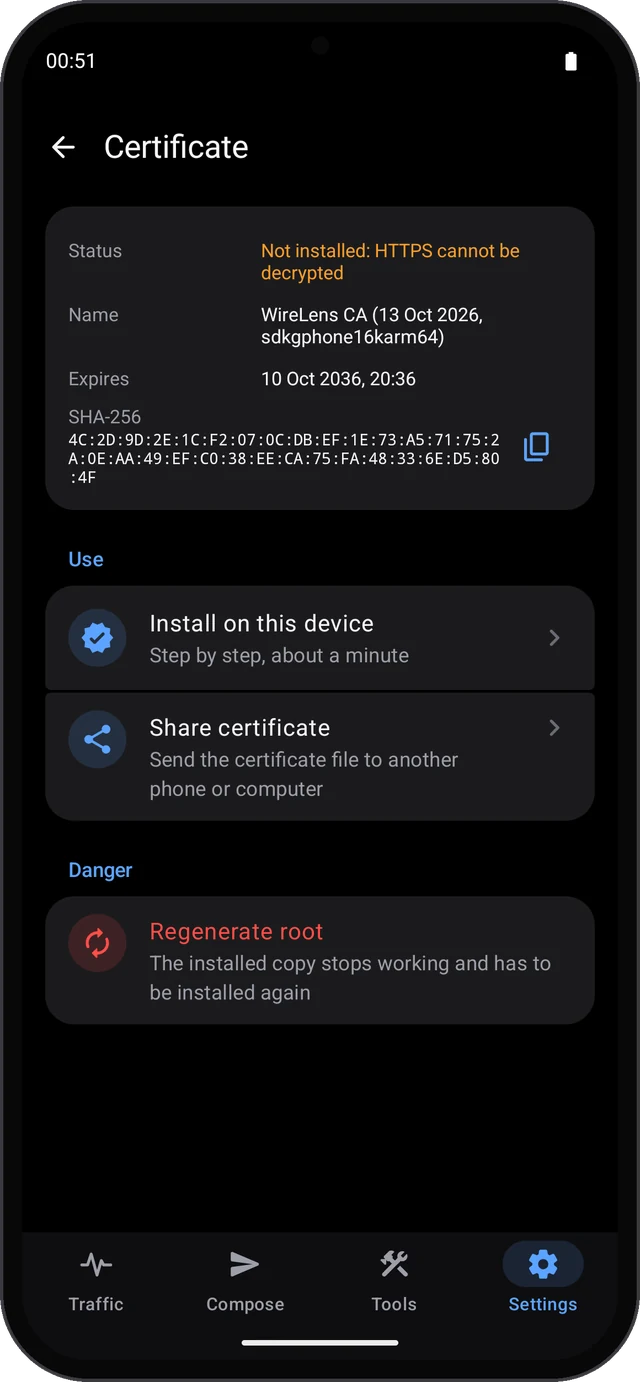
Android installs it as a user certificate. Browsers trust user certificates. Other apps trust them only if their developer opted in, so most third-party apps stay tunnelled; see Things Android decides.
Export, regenerate and remove#
| Mac | iPhone and iPad | Android | |
|---|---|---|---|
| Export | Certificate ▸ Export Root Certificate PEM… (WireLens-CA.pem) or DER… (WireLens-CA.cer) | Download the profile from the setup guide | Settings ▸ Certificate ▸ Share certificate |
| Regenerate | Settings ▸ Certificate ▸ Renew certificate ▸ Renew… | Settings ▸ Danger Zone ▸ Regenerate Root CA | Settings ▸ Certificate ▸ Renew certificate |
| Remove | Certificate ▸ Remove Certificate from Keychain…, or Settings ▸ Certificate ▸ Remove from the keychain ▸ Uninstall… | Settings ▸ General ▸ VPN & Device Management, the WireLens profile, Remove Profile | Android Settings ▸ Security & privacy ▸ More security & privacy ▸ Encryption & credentials ▸ User credentials, the WireLens entry, Remove |
Regenerating creates a new certificate. Everything that trusted the old one has to trust the new one, so only do it if you have a reason. Uninstalling WireLens does not remove the certificate.
If you stop using WireLens, remove the trust. There is no reason to keep trusting a certificate you are not using.
Bring your own#
Teams that already run their own certificate authority can import theirs instead of using the one WireLens made. See Client certificates and custom roots.
Something here is unclear, or wrong for your setup? Contact support or write to support@wirelens.app.