DNS Spoofing
Send a hostname to an address you choose, for testing a server before its DNS changes or pointing an app at a machine on your network.
DNS Spoofing sends a hostname to an address you pick. Use it to try a new server before its DNS record changes, to test one edge location, or to point an app at a machine on your network without changing the app.
What it does on each platform#
- Mac: WireLens connects to your address instead of the real one for matching captured hosts. The URL, the
Hostheader and the name in the TLS handshake stay the original name. Your Mac's own DNS is unchanged, and apps that do not go through WireLens are unaffected. - iPhone and iPad: WireLens answers the name lookup itself. A matching hostname then resolves to your address for every app on the device while capture runs.
- Android: WireLens answers the name lookup itself for every app it captures. Apps that use their own encrypted DNS are not affected.
Add a rule#
- Mac: open Tools ▸ DNS Spoof and click Add Rule.
- iPhone and iPad: open Tools ▸ DNS Spoof and add a rule.
- Android: long-press a host or a request and choose DNS Spoof…, or open Tools ▸ DNS Spoof and tap New override.
A rule is a host and the address to use for it. The host can be a name such as api.example.com or a wildcard such as *.cdn.example.com. The first enabled rule whose host matches wins. A blank host or a bare * matches nothing.
On the Mac#
Enable DNS Spoof is the master switch. While it is off, rules are kept but not applied. Each rule has a Host and either Map to IPv4 or Or hostname. A hostname target is looked up when the connection is made, and it takes priority over Map to IPv4 when both are set.
On iPhone and iPad#
A rule has an Original Host and Map to Address. Under Advanced:
- IPv6 Address answers IPv6 lookups. Leave it empty and apps fall back to the IPv4 address.
- TTL (seconds) sets how long apps cache the answer, from 0 to 86400.
The original host can also be an IP address, such as 1.1.1.1 mapped to 8.8.8.8. WireLens then sends every TCP and UDP packet for that address to the new one, and the replies still look as if they came from the original.
On Android#
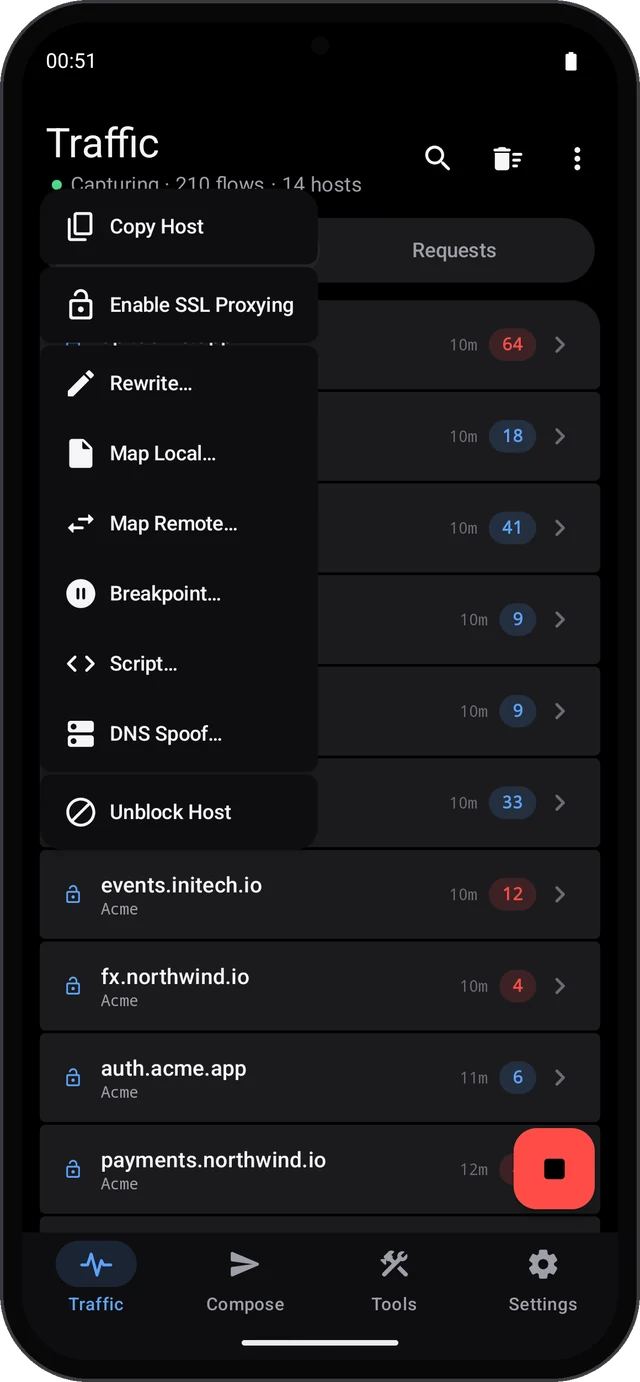
A rule has a Host and, under Answer with, an IPv4 address and an optional IPv6 address. Leave the IPv6 address empty to answer with no IPv6 address. Test a URL on the list shows which rule would answer for a host.
Tips#
- For HTTPS, the server at the new address must still present a certificate for the original hostname. A test server with a certificate for another name, or a self-signed one, fails the check. For a decrypted host on the Mac or iPhone, add an invalid origin certificate exception.
- To send traffic to a different hostname on the phone, or to change the path as well, use Map Remote.
Free and Pro#
The free plan includes one DNS Spoof rule on every platform. Pro removes the limit.
Command line and MCP#
The command line and the MCP server run on the Mac. wirelens ships inside the app and is not on your PATH until you link it once.
wirelens rules dns --pattern staging.example.com --ipv4 192.168.1.20
The MCP tool is add_dns_spoof, which takes spoof_ipv4, spoof_ipv6 or spoof_hostname, and a ttl.
Something here is unclear, or wrong for your setup? Contact support or write to support@wirelens.app.